Thông tin liên hệ
- 036.686.3943
- admin@nguoicodonvn2008.info

Suricata là một công cụ phát hiện xâm nhập (IDS), ngăn chặn xâm nhập (IPS) và giám sát an ninh mạng (NSM) miễn phí và mã nguồn mở dành cho Linux. Nó sử dụng một tập hợp các chữ ký và quy tắc để kiểm tra và xử lý lưu lượng mạng. Khi phát hiện các gói đáng ngờ đối với bất kỳ số lượng service nào trên máy chủ, chúng sẽ bị chặn ngay lập tức.
Theo mặc định, Suricata hoạt động như một hệ thống phát hiện xâm nhập thụ động, quét lưu lượng truy cập trên máy chủ để tìm các gói đáng ngờ. Tuy nhiên, bạn cũng có thể sử dụng nó như một hệ thống ngăn chặn xâm nhập chủ động (IPS) để ghi nhật ký, báo cáo và chặn hoàn toàn lưu lượng truy cập mạng tuân theo các quy tắc nhất định.
Hướng dẫn này sẽ chỉ cho bạn cách cài đặt Suricata IDS trên máy chủ Rocky Linux của mình.
Suricata không có trong kho lưu trữ mặc định của Rocky Linux. Vì vậy, bạn cần cài đặt nó từ kho EPEL.
Đầu tiên, cài đặt kho EPEL bằng lệnh sau:
dnf install epel-release -y
Sau khi EPEL được cài đặt, hãy kiểm tra thông tin gói Suricata bằng lệnh sau:
dnf info suricata
Bạn sẽ nhận được kết quả đầu ra sau:
Available Packages
Name         : suricata
Version      : 5.0.8
Release      : 1.el8
Architecture : x86_64
Size         : 2.3 M
Source       : suricata-5.0.8-1.el8.src.rpm
Repository   : epel
Summary      : Intrusion Detection System
URL          : https://suricata-ids.org/
License      : GPLv2
Description  : The Suricata Engine is an Open Source Next Generation Intrusion
             : Detection and Prevention Engine. This engine is not intended to
             : just replace or emulate the existing tools in the industry, but
             : will bring new ideas and technologies to the field. This new Engine
             : supports Multi-threading, Automatic Protocol Detection (IP, TCP,
             : UDP, ICMP, HTTP, TLS, FTP and SMB! ), Gzip Decompression, Fast IP
             : Matching, and GeoIP identification.
Tiếp theo, cài đặt Suricata bằng lệnh sau:
dnf install suricata -y
Sau khi cài đặt thành công, bạn có thể tiến hành bước tiếp theo.
Suricata chứa nhiều quy tắc gọi là signature để phát hiện các mối đe dọa. Tất cả các quy tắc đều nằm trong thư mục /etc/suricata/rules/.
Chạy lệnh sau để liệt kê tất cả các quy tắc:
ls /etc/suricata/rules/
Bạn sẽ nhận được kết quả đầu ra sau:
app-layer-events.rules  dnp3-events.rules  http-events.rules      modbus-events.rules  smb-events.rules     tls-events.rules
decoder-events.rules    dns-events.rules   ipsec-events.rules     nfs-events.rules     smtp-events.rules
dhcp-events.rules       files.rules        kerberos-events.rules  ntp-events.rules     stream-events.rules
Tiếp theo, chạy lệnh sau để cập nhật tất cả các quy tắc:
suricata-update
Bạn sẽ nhận được kết quả đầu ra sau:
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/app-layer-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/decoder-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/dhcp-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/dnp3-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/dns-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/files.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/http-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/ipsec-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/kerberos-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/modbus-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/nfs-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/ntp-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/smb-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/smtp-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/stream-events.rules
19/9/2023 -- 05:28:15 -  -- Loading distribution rule file /usr/share/suricata/rules/tls-events.rules
19/9/2023 -- 05:28:15 -  -- Ignoring file rules/emerging-deleted.rules
19/9/2023 -- 05:28:20 -  -- Loaded 32403 rules.
19/9/2023 -- 05:28:20 -  -- Disabled 14 rules.
19/9/2023 -- 05:28:20 -  -- Enabled 0 rules.
19/9/2023 -- 05:28:20 -  -- Modified 0 rules.
19/9/2023 -- 05:28:20 -  -- Dropped 0 rules.
19/9/2023 -- 05:28:21 -  -- Enabled 131 rules for flowbit dependencies.
19/9/2023 -- 05:28:21 -  -- Backing up current rules.
19/9/2023 -- 05:28:26 -  -- Writing rules to /var/lib/suricata/rules/suricata.rules: total: 32403; enabled: 25008; added: 0; removed 0; modified: 0
19/9/2023 -- 05:28:27 -  -- Writing /var/lib/suricata/rules/classification.config
19/9/2023 -- 05:28:27 -  -- No changes detected, exiting.
Tiếp theo, chỉnh sửa file cấu hình Suricata và xác định IP máy chủ, đường dẫn quy tắc và interface mạng của bạn:
nano /etc/suricata/suricata.yaml
Thay đổi các dòng sau:
  #HOME_NET: "[192.198.0.0/19,10.0.0.0/8,172.19.0.0/12]"
    HOME_NET: "[192.198.1.48]"
    #HOME_NET: "[192.198.0.0/19]"
    #HOME_NET: "[10.0.0.0/8]"
    #HOME_NET: "[172.19.0.0/12]"
    #HOME_NET: "any"

    EXTERNAL_NET: "!$HOME_NET"
    #EXTERNAL_NET: "any"

af-packet:
  - interface: eth0

default-rule-path: /var/lib/suricata/rules

rule-files:
  - suricata.rules
Lưu và đóng file khi bạn hoàn tất và tắt tính năng offload bằng lệnh sau:
ethtool -K eth0 gro off lro off
Tiếp theo, khởi động service Suricata và kích hoạt nó bằng lệnh sau để nó mở khi hệ thống được khởi động lại:
systemctl start suricata
systemctl enable suricata
Bạn có thể kiểm tra trạng thái của Suricata bằng lệnh sau:
systemctl status suricata
Bạn sẽ nhận được kết quả đầu ra sau:
? suricata.service - Suricata Intrusion Detection Service
   Loaded: loaded (/usr/lib/systemd/system/suricata.service; enabled; vendor preset: disabled)
   Active: active (running) since Wed 2022-03-19 10:06:20 UTC; 5s ago
     Docs: man:suricata(1)
  Process: 24047 ExecStartPre=/bin/rm -f /var/run/suricata.pid (code=exited, status=0/SUCCESS)
 Main PID: 24049 (Suricata-Main)
    Tasks: 1 (limit: 23696)
   Memory: 232.9M
   CGroup: /system.slice/suricata.service
           ??24049 /sbin/suricata -c /etc/suricata/suricata.yaml --pidfile /var/run/suricata.pid -i eth0 --user suricata

Sep 19 10:06:20 rockylinux systemd[1]: Starting Suricata Intrusion Detection Service...
Sep 19 10:06:20 rockylinux systemd[1]: Started Suricata Intrusion Detection Service.
Sep 19 10:06:20 rockylinux suricata[24049]: 19/9/2023 -- 10:06:20 -  - This is Suricata version 5.0.8 RELEASE running in SYSTEM mode
Để kiểm tra nhật ký tiến trình Suricata, hãy chạy lệnh sau:
tail /var/log/suricata/suricata.log
Bạn sẽ thấy đầu ra sau:
19/9/2023 -- 10:06:23 -  - Running in live mode, activating unix socket
19/9/2023 -- 10:06:23 -  - SSSE3 support not detected, disabling Hyperscan for SPM
19/9/2023 -- 10:06:23 -  - 1 rule files processed. 24930 rules successfully loaded, 0 rules failed
19/9/2023 -- 10:06:23 -  - Threshold config parsed: 0 rule(s) found
19/9/2023 -- 10:06:23 -  - 24933 signatures processed. 1283 are IP-only rules, 4109 are inspecting packet payload, 19340 inspect application layer, 105 are decoder event only
19/9/2023 -- 10:06:23 -  - Going to use 2 thread(s)
19/9/2023 -- 10:06:23 -  - Running in live mode, activating unix socket
19/9/2023 -- 10:06:23 -  - Using unix socket file '/var/run/suricata/suricata-command.socket'
19/9/2023 -- 10:06:23 -  - all 2 packet processing threads, 4 management threads initialized, engine started.
19/9/2023 -- 10:06:23 -  - All AFP capture threads are running.
Bạn có thể kiểm tra nhật ký cảnh báo Suricata bằng lệnh sau:
tail -f /var/log/suricata/fast.log
Bạn sẽ thấy đầu ra sau:
19/19/2022-10:06:23.059177  [**] [1:2402000:6215] ET DROP Dshield Block Listed Source group 1 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 45.155.205.43:54612 -> 209.23.8.4:14381
09/19/2023-10:06:23.059177  [**] [1:2403342:73004] ET CINS Active Threat Intelligence Poor Reputation IP group 43 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 45.155.205.43:54612 -> 209.23.8.4:14381
Để kiểm tra nhật ký thống kê Suricata, hãy sử dụng lệnh sau:
tail -f /var/log/suricata/stats.log
Bạn sẽ thấy đầu ra sau:
------------------------------------------------------------------------------------
Counter                                       | TM Name                   | Value
------------------------------------------------------------------------------------
capture.kernel_packets                        | Total                     | 651
decoder.pkts                                  | Total                     | 651
decoder.bytes                                 | Total                     | 51754
decoder.ipv4                                  | Total                     | 398
decoder.ipv6                                  | Total                     | 251
decoder.ethernet                              | Total                     | 651
Sau khi cài đặt Suricata IDS, bạn cũng cần kiểm tra xem Suricata IDS có hoạt động hay không. Để thực hiện việc này, hãy đăng nhập vào hệ thống khác và cài đặt tiện ích hping3 để thực hiện cuộc tấn công DDoS.
dnf install hping3
Sau khi cài đặt hping3, hãy chạy lệnh sau để thực hiện tấn công DDoS:
hping3 -S -p 22 --flood --rand-source suricata-ip
Bây giờ hãy vào hệ thống Suricata và kiểm tra nhật ký cảnh báo bằng lệnh sau:
tail -f /var/log/suricata/fast.log
Bạn sẽ thấy đầu ra sau:
09/19/2023-10:08:18.049526  [**] [1:2403393:73004] ET CINS Active Threat Intelligence Poor Reputation IP group 94 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 89.248.193.194:44217 -> 209.23.8.4:37394
09/19/2023-10:08:52.933947  [**] [1:2402000:6215] ET DROP Dshield Block Listed Source group 1 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 197.248.133.173:24721 -> 209.23.8.4:9307
09/19/2023-10:09:52.284374  [**] [1:2402000:6215] ET DROP Dshield Block Listed Source group 1 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 89.248.195.202:57104 -> 209.23.8.4:6061
09/19/2023-10:10:52.284374  [**] [1:2403393:73004] ET CINS Active Threat Intelligence Poor Reputation IP group 94 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 89.248.195.202:57104 -> 209.23.8.4:6061
09/19/2023-10:10:19.951353  [**] [1:2403341:73004] ET CINS Active Threat Intelligence Poor Reputation IP group 42 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 45.137.21.208:42694 -> 209.23.8.4:57335
09/19/2023-10:11:21.477358  [**] [1:2403369:73004] ET CINS Active Threat Intelligence Poor Reputation IP group 70 [**] [Classification: Misc Attack] [Priority: 2] {TCP} 61.190.237.40:48539 -> 209.23.8.4:2375
Nguồn tin: Quantrimang.com
Ý kiến bạn đọc
Những tin mới hơn
 Kiên trì là chìa khóa để thành công (30/10/2023)
 Niềm say mê và sự bứt phá (30/10/2023)
 Cách biến text thành video bằng Runway Gen 2 (30/10/2023)
 Tiny11 core, phiên bản Windows 11 chỉ nặng 2GB, chạy mượt trên PC 4GB RAM (30/10/2023)
 Điều kiện BETWEEN trong SQL Server (31/10/2023)
 Cách tạo khung viền trong PowerPoint (31/10/2023)
 Tình cảm tuổi học trò phải chăng là thứ tình cảm đẹp đẽ nhất? (01/11/2023)
 7 widget Windows 11 tốt nhất cho năng suất (01/11/2023)
 10 cách mở applet Control Panel Windows Firewall trong Windows 11 (01/11/2023)
Những tin cũ hơn
 FUNCTION (Hàm) trong SQL Server (27/10/2023)
 Cách kích hoạt Dark Mode cho trình duyệt Edge (27/10/2023)
 Hướng dẫn dùng Copilot trên trình duyệt Microsoft Edge (27/10/2023)
 Thẻ HTML (26/10/2023)
 Tổng hợp các cách mở File Explorer trên Windows 11 (26/10/2023)
 File CRDOWNLOAD là gì? (26/10/2023)
 Mệnh đề PIVOT trong SQL Server (26/10/2023)
 20 bài học thực tế về cuộc sống giúp bạn sống tốt và ý nghĩa hơn (26/10/2023)
 Hàm input() trong Python (26/10/2023)
 Cách tính lãi suất bằng hàm RATE trong Excel (26/10/2023)
 Agent hỗ trợ nhiều giọng nói trong ElevenAgents
 Kết hợp các kỹ thuật tạo prompt để thực hiện dự án thực tế
 Xây dựng agent dựa trên flow, an toàn cho môi trường Production
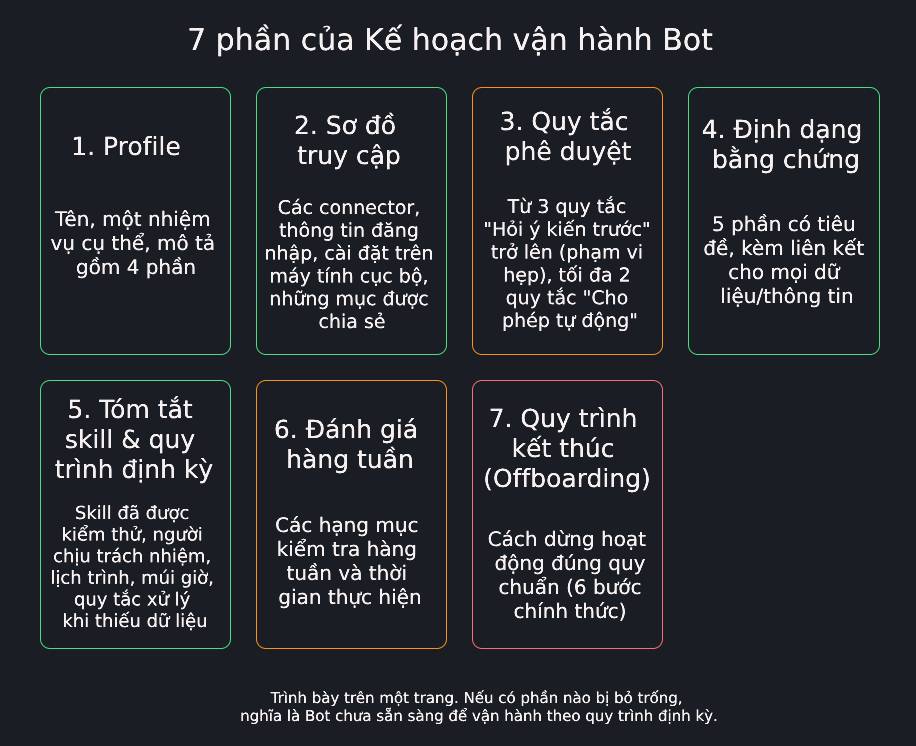 Tạo kế hoạch vận hành Bot có giám sát trong Grok Bot
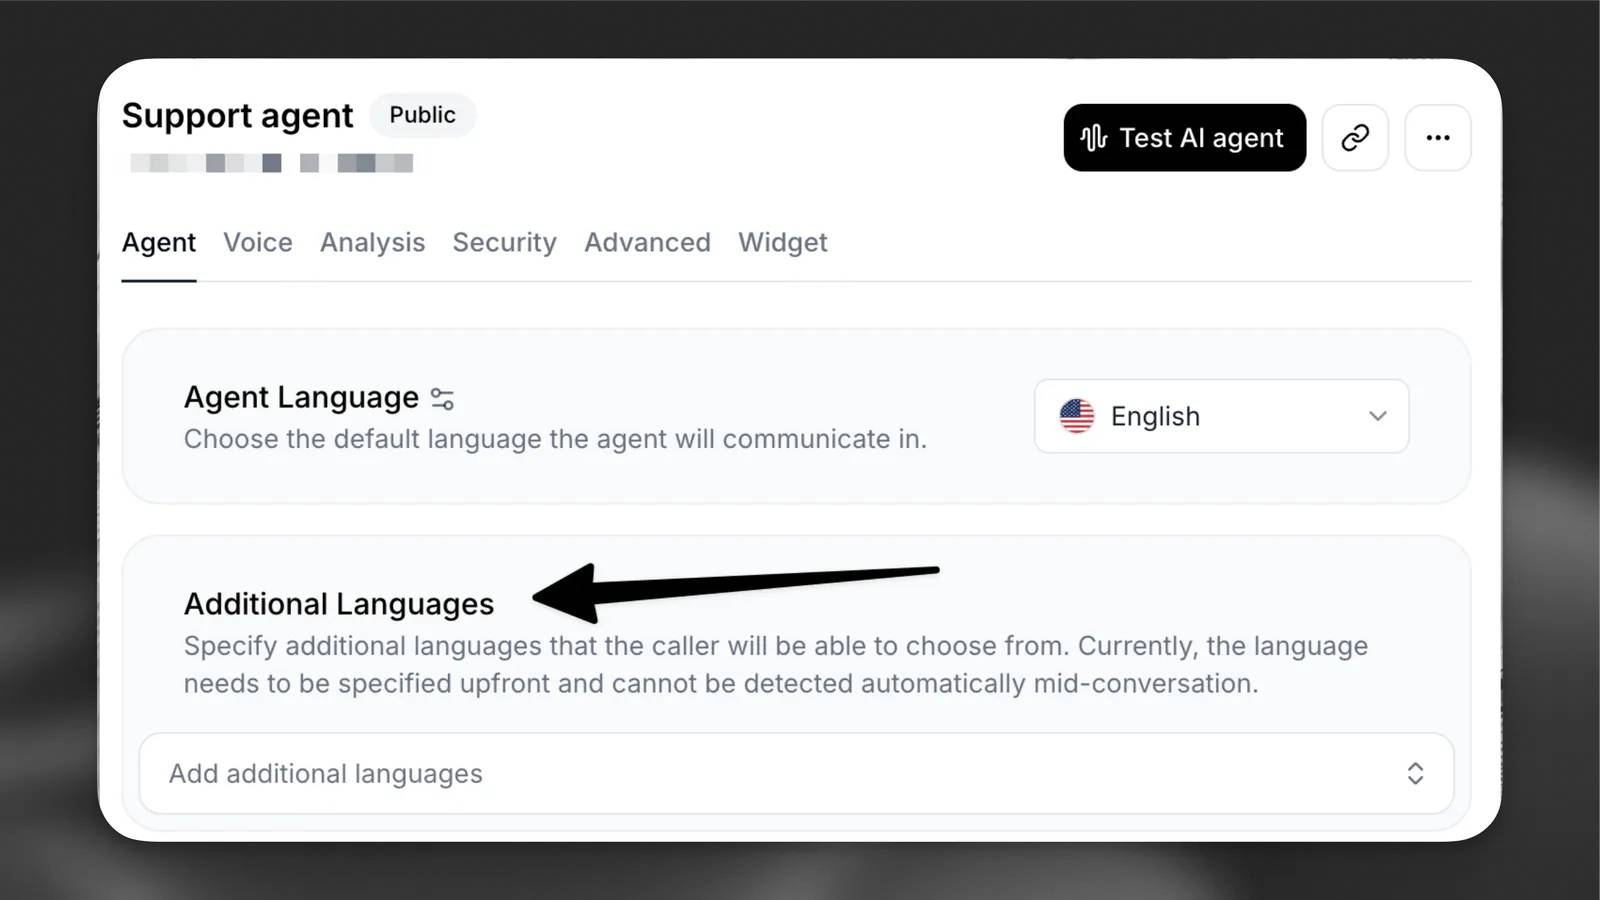 Cách cấu hình agent để giao tiếp bằng nhiều ngôn ngữ trong ElevenAgents
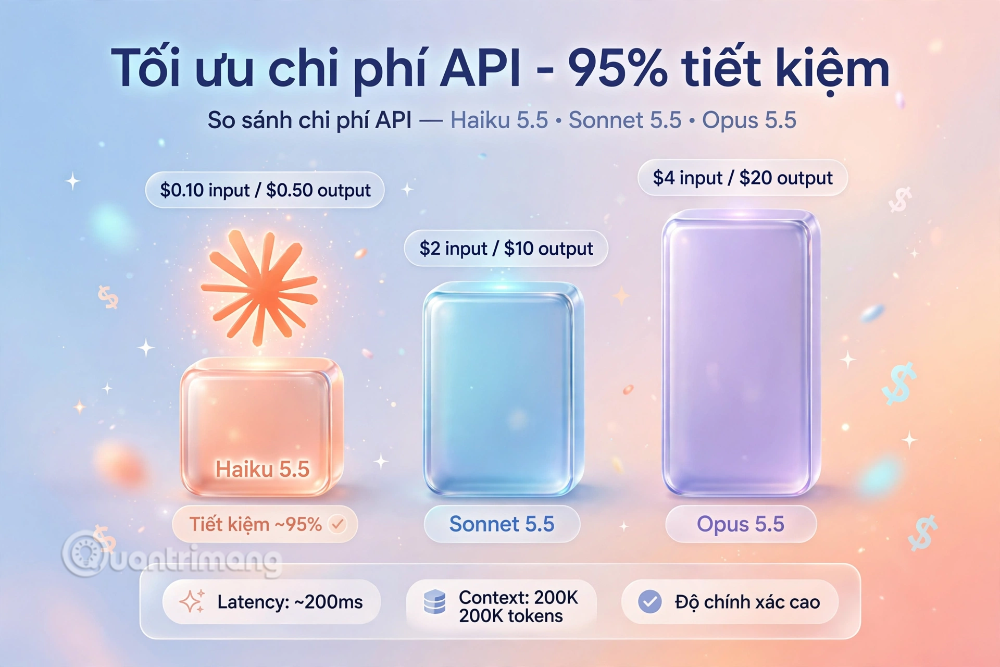 Hướng dẫn dùng Claude Haiku 5.5 làm trợ lý phân loại trong Claude Code
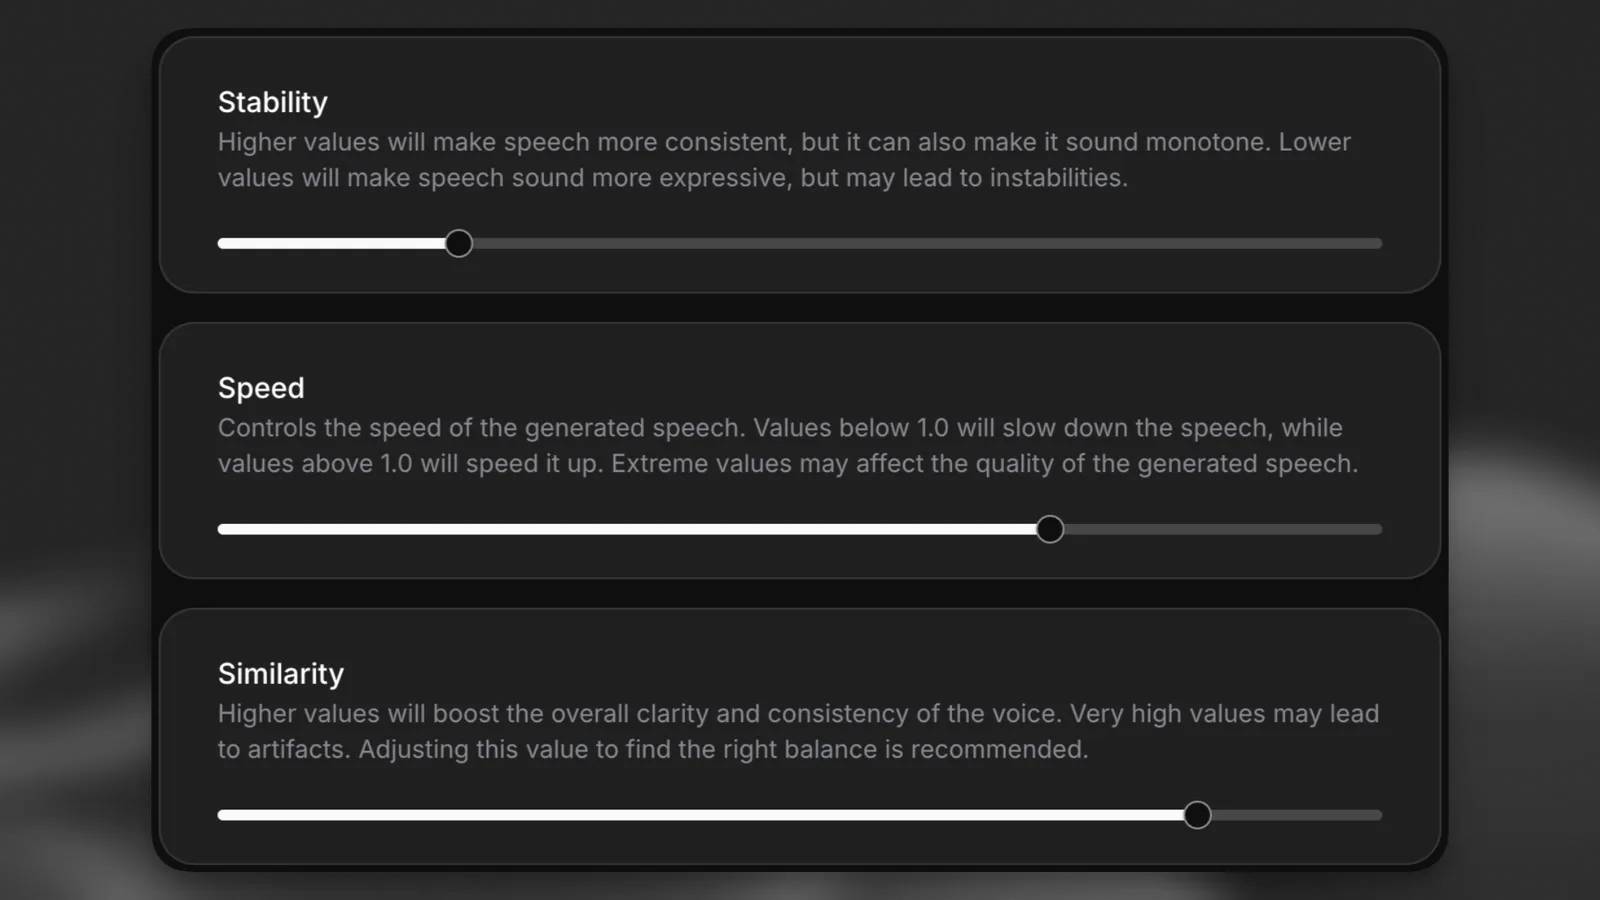 Cách thiết kế giọng nói sống động, lôi cuốn cho ElevenLabs Agents
 Cách kết nối Google Drive với Gemini Spark đọc và xử lý tài liệu
 Chế độ Sinh viên trong Gemini: Không gian học tập có lộ trình
 Cách biến ý tưởng thành thiết kế bằng MagicPath trong ChatGPT
 TOP công cụ AI tạo workflow tốt nhất
 TOP trình duyệt web AI tốt nhất
 Cách cung cấp kiến thức phù hợp cho agent trong Microsoft Copilot Studio
 Thiết lập cơ sở kiến thức cho ElevenAgents
 15 prompt AI thú vị cho ngày lễ Halloween
 Hướng dẫn chat bằng giọng nói trên Dola AI
 Top công cụ AI tốt nhất cho Digital Marketing
 Hướng dẫn tạo giọng nói cá nhân trên Dola AI
 tOP plugin ChatGPT tốt nhất để lên kế hoạch du lịch
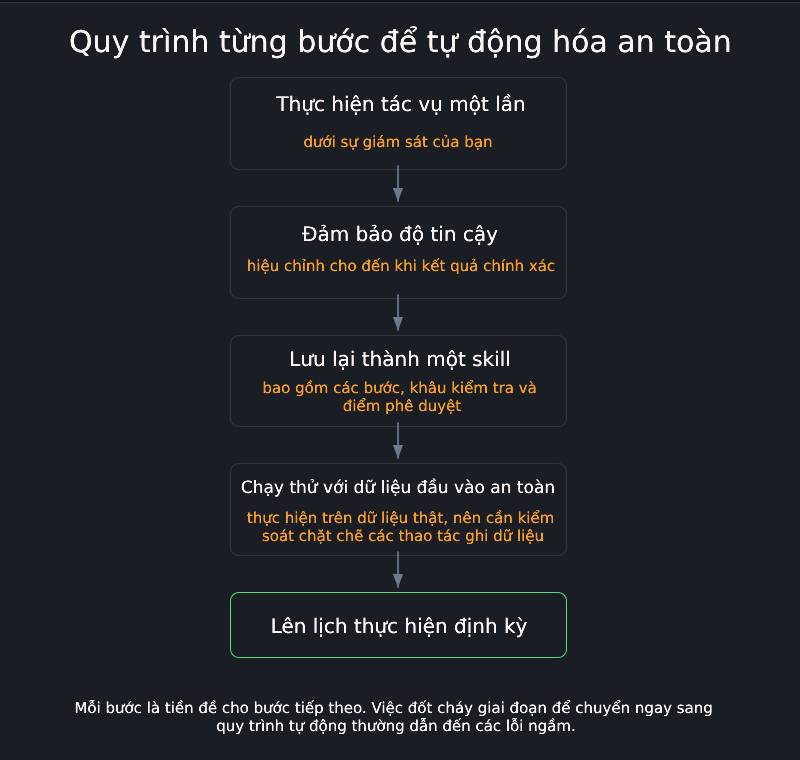 Trình tự đảm bảo tính an toàn cho quy trình tự động hóa trong Grok Bot
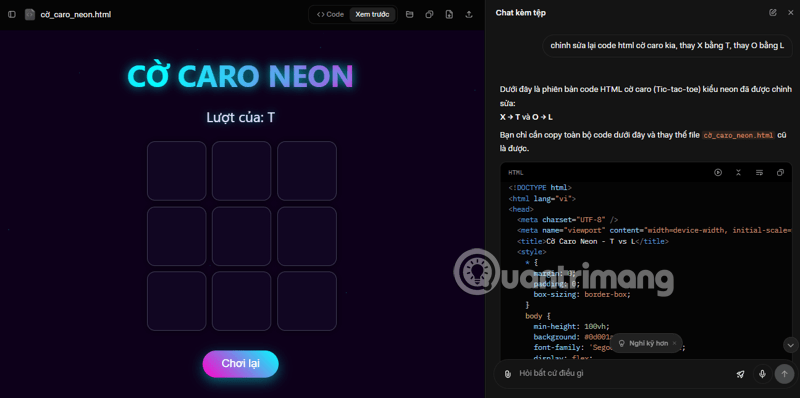 Cách lập trình chuyên nghiệp hơn, dễ dàng hơn với tính năng Tệp trên Grok
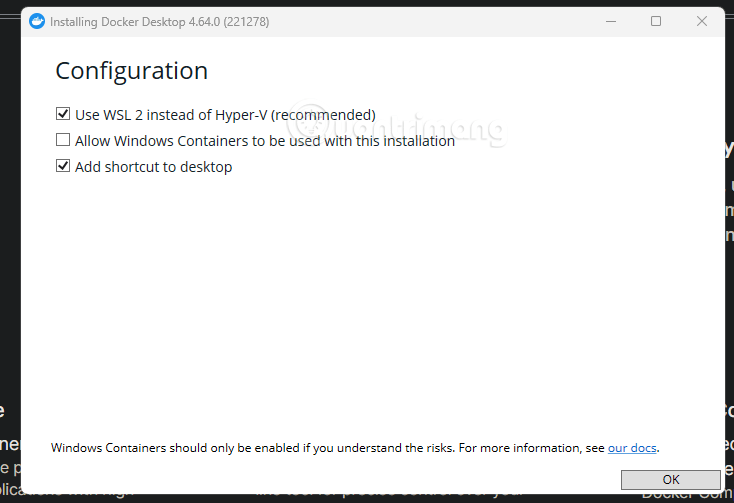 Hướng dẫn cài đặt và sử dụng n8n trên Windows 11
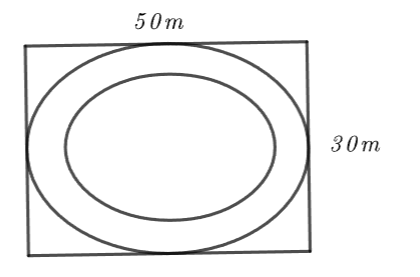 Công thức tính diện tích hình Elip
 Hướng dẫn ngắt kết nối ứng dụng trên ChatGPT
 Hướng dẫn tạo đoạn hội thoại cho topic trên Twee
 6 cách mở Computer/System Properties trong Windows 10
 Đừng chia sẻ ảnh cho đến khi bạn chạy kiểm tra siêu dữ liệu này!
 Bức tranh tổng quan về hỗ trợ khách hàng tích hợp AI
 Cách sửa lỗi There Are Currently No Power Options Available Windows
 Hướng dẫn 8 cách mở bàn phím ảo trên Windows 10